Quickstart
Get started with emitd in under five minutes. Choose your path — integrate via our edge REST API and SDKs, or send and manage broadcasts directly from the no-code Console.
Whether you are an engineer integrating transactional emails into a web application or a marketer launching high-converting broadcast campaigns, emitd gets your emails to the inbox with sub-second delivery.
Choose your preferred onboarding track below:
Send your first email with one API call — no complex build step required.
1. Get an API key
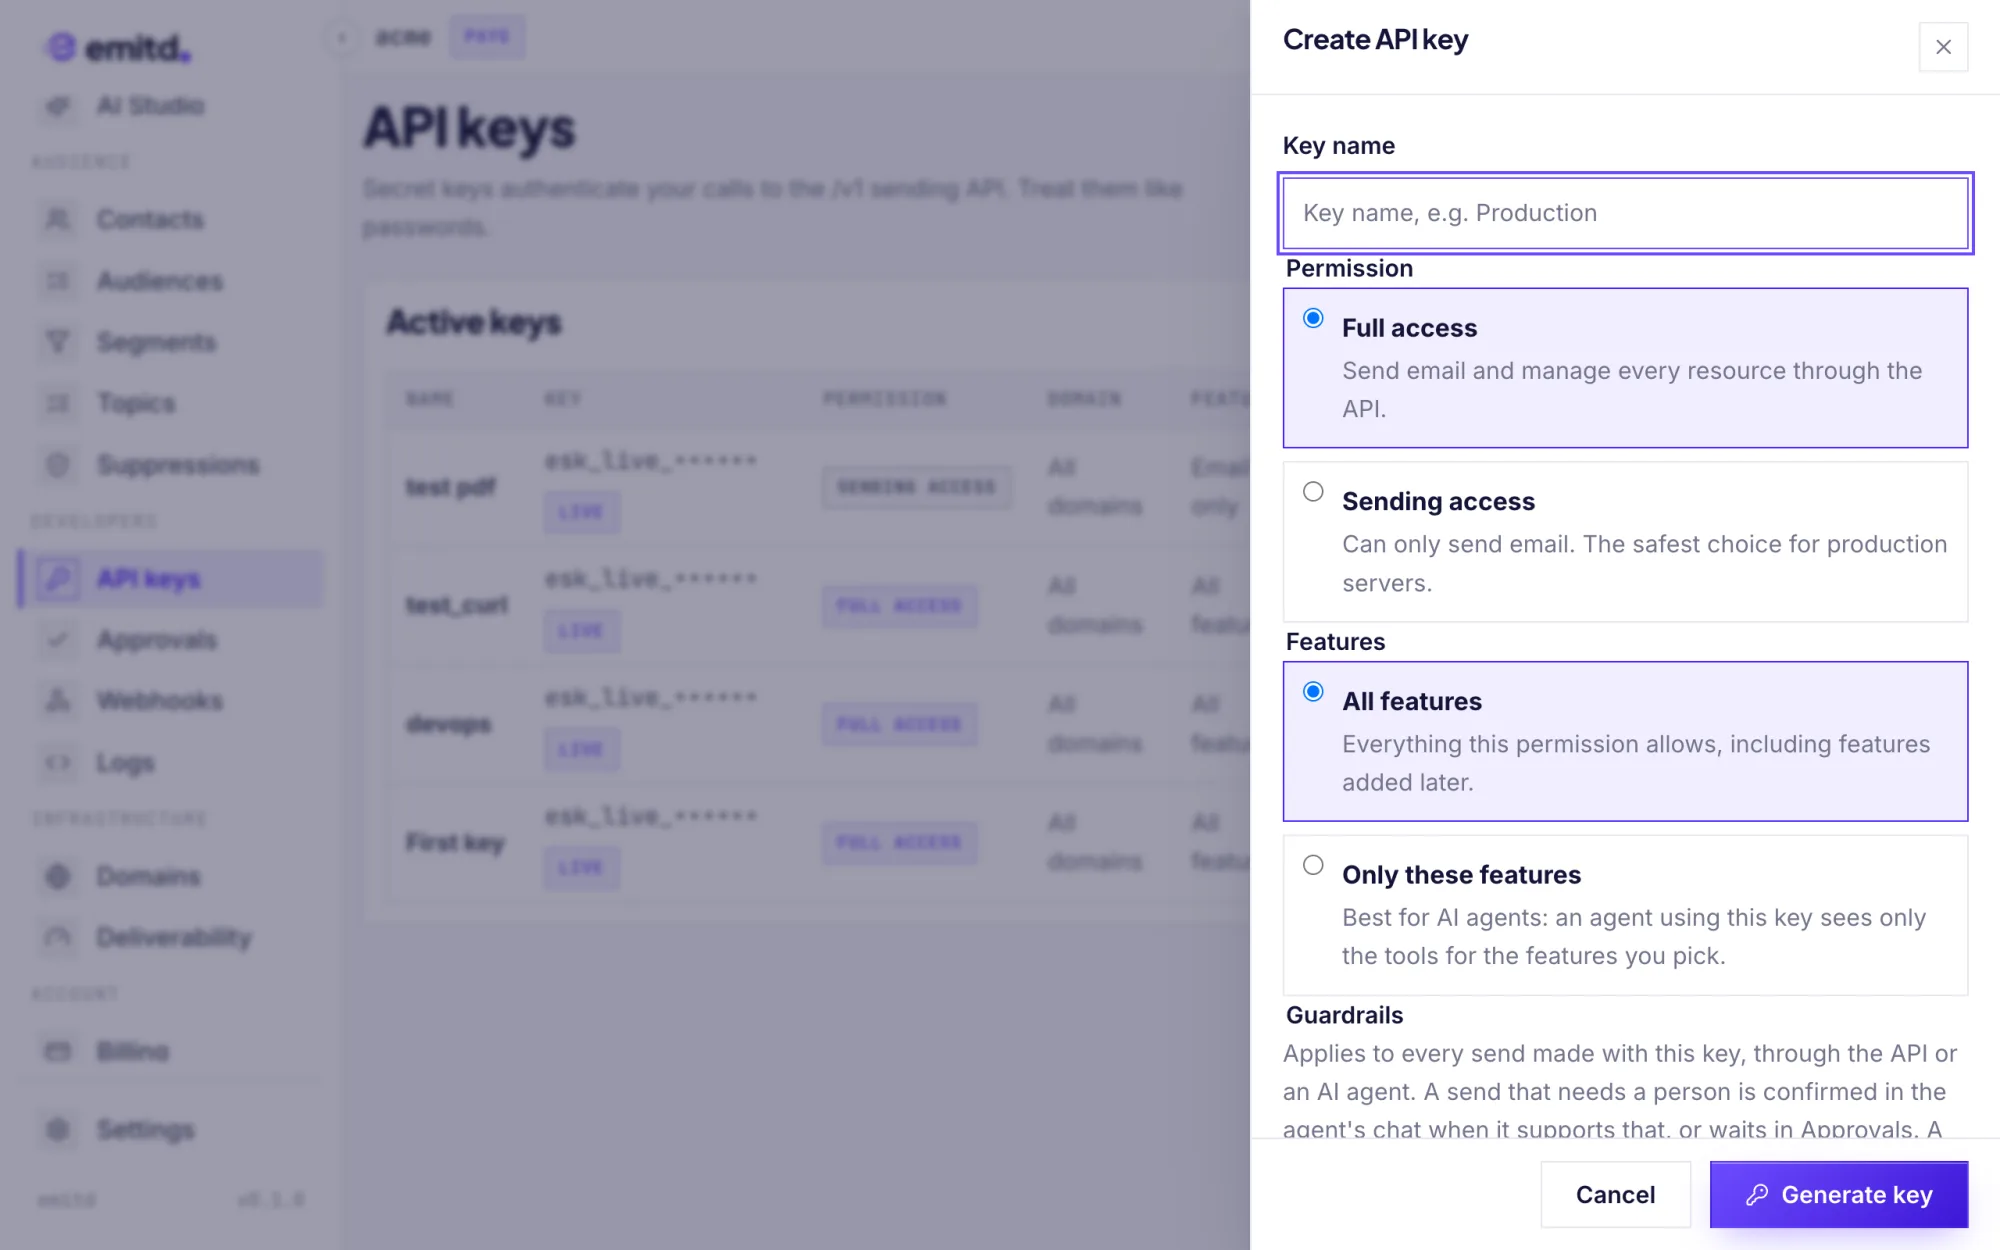
Create an API key in the Console under API keys:
- Click Create key and give it a descriptive name (e.g.,
prod-backendorci-tests). - Select Sending access for production application servers (or Full access for CI/CD pipelines).
- Optionally configure rate limit guardrails to prevent accidental runaway loops.
- Click Generate key.
Store your key securely
The key is displayed in full exactly once. Store it in your secrets manager or export it to your local environment:
export EMITD_API_KEY=esk_live_...2. Verify your sending domain
To protect your inbox reputation and prevent spoofing, emitd requires sender domain verification. In the Console under Domains:
- GoDaddy, IONOS, 1&1, Squarespace: Click Set up in one click to configure DNS automatically via Domain Connect.
- Cloudflare: Click Auto configure to publish records instantly using a scoped API token.
- Other DNS providers (Route 53, Namecheap, Google Cloud DNS): Copy the SPF, DKIM (2048-bit RSA or CNAMEs), and DMARC records shown, or download the pre-built RFC 1035 zone file.
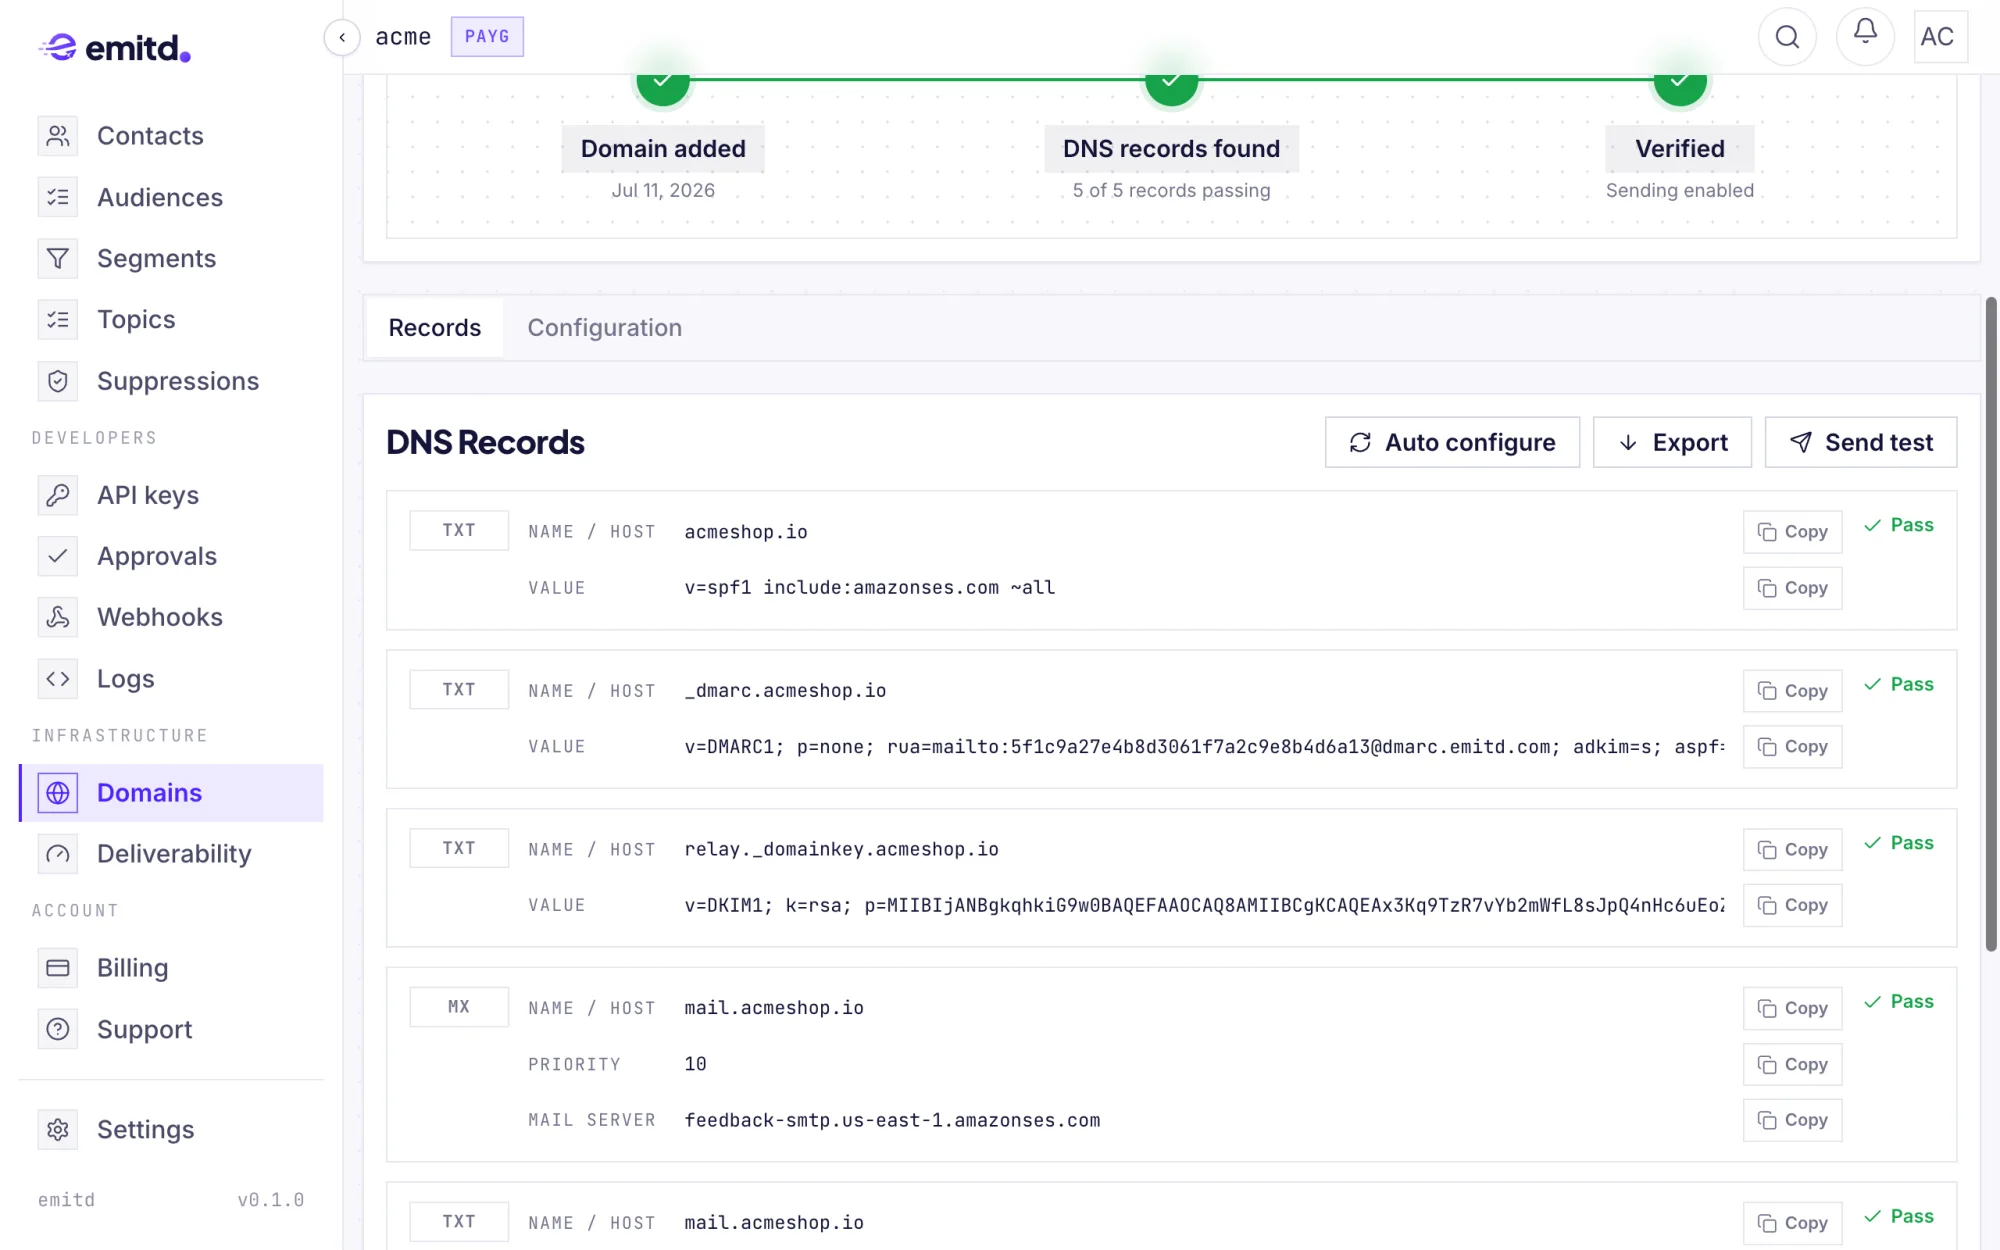
Verification typically finishes in under 2 minutes. Until verified, production sends from that domain fail with from_domain_not_verified — see Sending domains.
3. Send your first email
Dispatch your first email through the edge REST API (https://api.emitd.com/v1/email):
curl https://api.emitd.com/v1/email \
  -H "Authorization: Bearer $EMITD_API_KEY" \
  -H "Content-Type: application/json" \
  -d '{
    "from": "hello@yourdomain.com",
    "to": ["user@example.com"],
    "subject": "Welcome to our platform!",
    "html_body": "<h1>Welcome aboard!</h1><p>We are thrilled to have you with us.</p>",
    "text_body": "Welcome aboard! We are thrilled to have you with us.",
    "message_stream": "outbound"
  }'
Response shape
Every valid send returns an immediate 202 Accepted response:
HTTP/2 202
{
  "message_id": "msg_2h8Kd0Rk9Qa",
  "status": "queued"
}
The 202 Accepted status indicates the message was validated at the edge and queued for high-speed delivery.
Safe retries with Idempotency-Key
Include an Idempotency-Key: <unique-id> header on any send request. If your network connection drops and your client retries, emitd replays the original 202 Accepted response rather than sending a duplicate email. See Idempotency.
4. Test without sending live emails
Test your end-to-end integration safely using Emitd's Sandbox without consuming sending quota or hitting live mailboxes:
curl https://api.emitd.com/v1/email \
  -H "Authorization: Bearer $EMITD_API_KEY" \
  -H "X-Relay-Test: true" \
  -H "Content-Type: application/json" \
  -d '{
    "from": "hello@yourdomain.com",
    "to": ["delivered@emitd.com"],
    "subject": "Sandbox test email",
    "html_body": "<p>Testing sandbox pipeline</p>"
  }'
Simulate various mailbox responses using reserved test addresses:
delivered@emitd.com: Fires a successfuldeliverywebhook.bounced@emitd.com: Fires a hardbouncewebhook and adds the recipient to your suppression test list.complained@emitd.com: Fires a spamcomplaintwebhook.
Inspect recent test executions with GET /v1/email/test-events. See Test mode.
5. Subscribe to delivery webhooks
Receive real-time signed notifications when emails are delivered, opened, clicked, or bounced:
- In the Console, navigate to Webhooks and click Add endpoint.
- Enter your HTTPS listener URL (e.g.
https://api.yourdomain.com/webhooks/emitd). - Select your desired events (
sent,delivery,bounce,complaint,open,click). - emitd signs every request with an
X-Webhook-Signature: sha256=<hex>header computed using HMAC-SHA256 over the raw request payload.
See Webhooks guide and API Recipes for signature verification code in Node.js, Python, and Go.
6. Connect AI agents via Model Context Protocol (MCP)
If you use Cursor, Claude Code, Windsurf, or custom autonomous LLM agents, connect them directly to Emitd's hosted MCP server at https://mcp.emitd.com/mcp. Your agent can draft templates, check domain health, analyze deliverability, and send emails within strict guardrails.
Emitd integration options
| Channel / Interface | Best For | Typical Latency | Key Features |
|---|---|---|---|
| Edge REST API | Web applications, SaaS backends, mobile APIs | < 45 ms | Sub-second dispatch, dual streams (outbound / broadcast), batching, idempotency |
| Official SDKs | TypeScript, Python, Go, Rust, Ruby, PHP, Java, .NET | < 45 ms | Type-safe models, built-in retry logic, automatic HMAC signature verification |
| Model Context Protocol (MCP) | Cursor, Claude Code, Windsurf, autonomous LLMs | Real-time | Tool calling, natural language template generation, domain inspection, deliverability diagnostics |
| No-Code Console | Marketers, founders, product managers | Instant | 1-Click Domain Connect, visual AI Template Studio, CSV subscriber imports, broadcast scheduling |
| SMTP Relay | WordPress, legacy ERPs, existing mail clients | Standard | Drop-in credentials (smtp.emitd.com:587), TLS 1.3 encryption, automatic suppression checks |
Next steps
Send an email
Body parameters, templates, scheduling, attachments, and headers.
API Recipes & Code Patterns
Production-ready snippets for OTPs, receipts, templates, attachments, and bulk sends.
Sending domains & DNS
1-Click Domain Connect, Cloudflare auto-publish, and manual DNS setup.
Email deliverability
SPF, DKIM, DMARC, Return-Path, and Google/Yahoo sender requirements.
Webhooks
Get delivery, bounce, and complaint events signed to your endpoint.
AI agents & MCP
Connect Cursor or Claude Code to emitd's hosted MCP server.
Broadcasts & Campaigns
Design, segment, and schedule marketing newsletters to your audience.
Migration guides
Step-by-step cutover from SendGrid, Resend, Postmark, and AWS SES.
Introduction
emitd is the modern email infrastructure platform for every use case — transactional, marketing, automations, inbound parsing, and AI agents. Sub-second edge delivery, 1-click Domain Connect DNS, and 9 native SDKs.
Authentication
API keys, permission scopes, and domain-scoped keys for the emitd API.